GRC and compliance management connected to everyday IT work
The GRC & Compliance suite shows where you stand against each framework, which controls are implemented, who owns them and what evidence backs them up. Evidence comes from real platform activity rather than spreadsheets assembled before an audit.
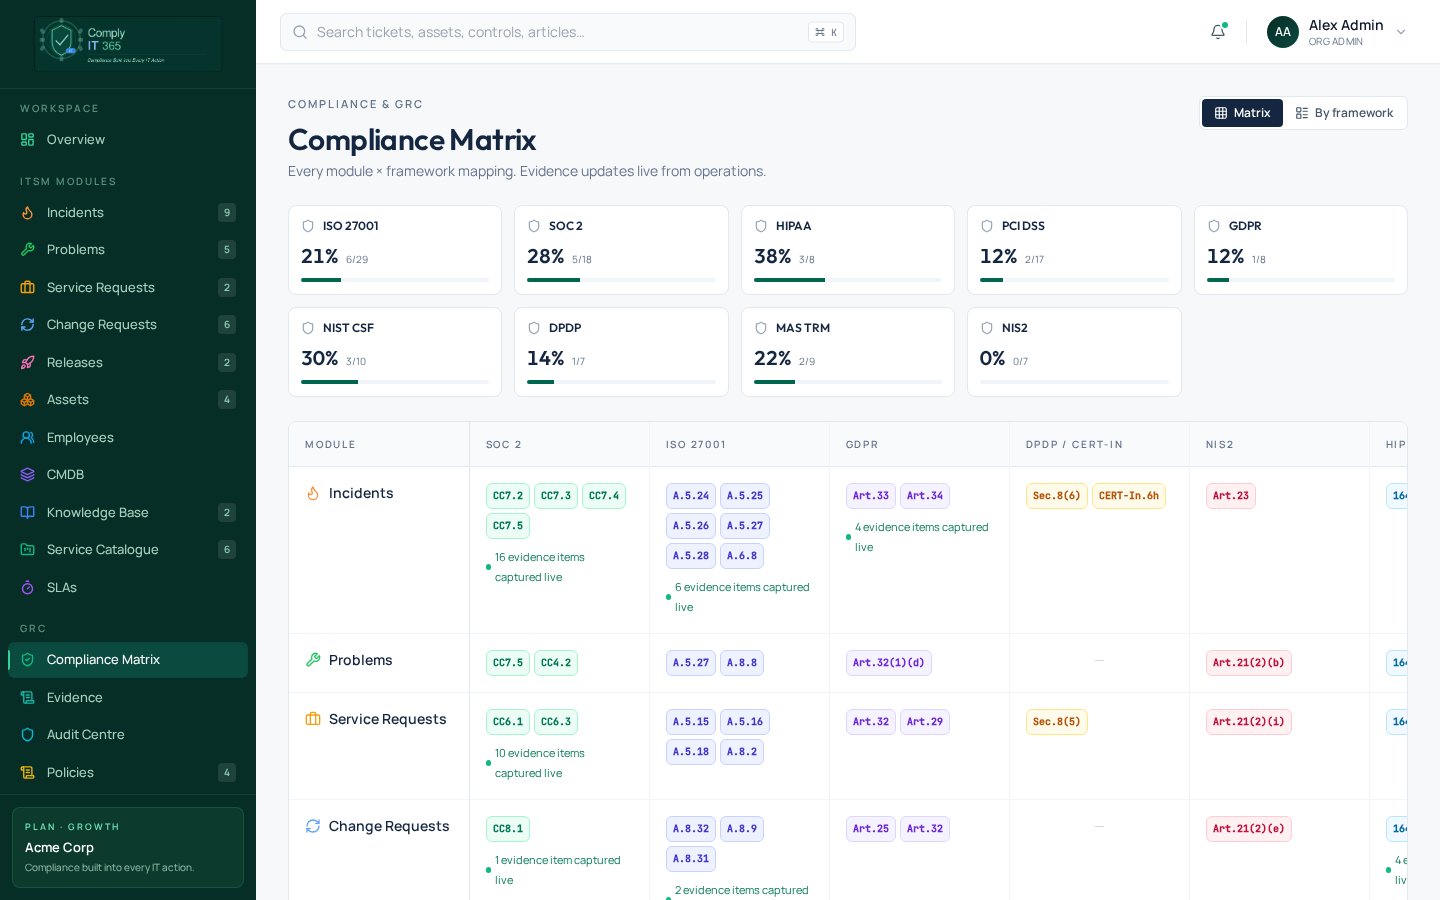
Compliance capabilities
Compliance matrix
A module-by-framework view of control coverage, with a deep dive into each framework's controls and their status.
Controls and ownership
Assign owners, set status from not started to verified, and open any control to see the linked incidents, changes, assets and evidence.
Evidence
Evidence records are created from platform actions and uploads and linked to one or more controls, so one activity can support several frameworks.
Policies
Maintain policies with owners, review dates and status.
Risk register
Record risks with likelihood and impact scoring, treatment plans, owners and residual risk.
Audit Centre
Review the platform audit trail and recent activity across modules in one place.
Built around recognised frameworks
ComplyIT365 ships with 16 framework packs, including SOC 2, ISO 27001, ISO 42001, HIPAA, PCI DSS 4.0, GDPR and DPDPA.
Third-party risk is part of GRC
Vendor risk feeds the same programme. Vendor assessments, findings and remediation live in Vendor365 and sit alongside your internal controls.